Financial Services
Financial Services

Cybersecurity and Compliance for Institutions That Move Money

One approved wire, one compromised advisor login, or one missed notification deadline can undo years of relationship building. Financial institutions carry that risk every day, and they answer to more regulators than almost any other industry.

Centaris supports community banks, credit unions, registered investment advisers, and independent insurance agencies throughout the Great Lakes states. We bring security, managed IT, and Microsoft expertise shaped by the frameworks you answer to, from GLBA and Regulation S-P to NCUA rules and Michigan's insurance data security law.

Examiners, auditors, and carriers all want the same thing: evidence that your controls work. We help you build that evidence and maintain it through every exam cycle.

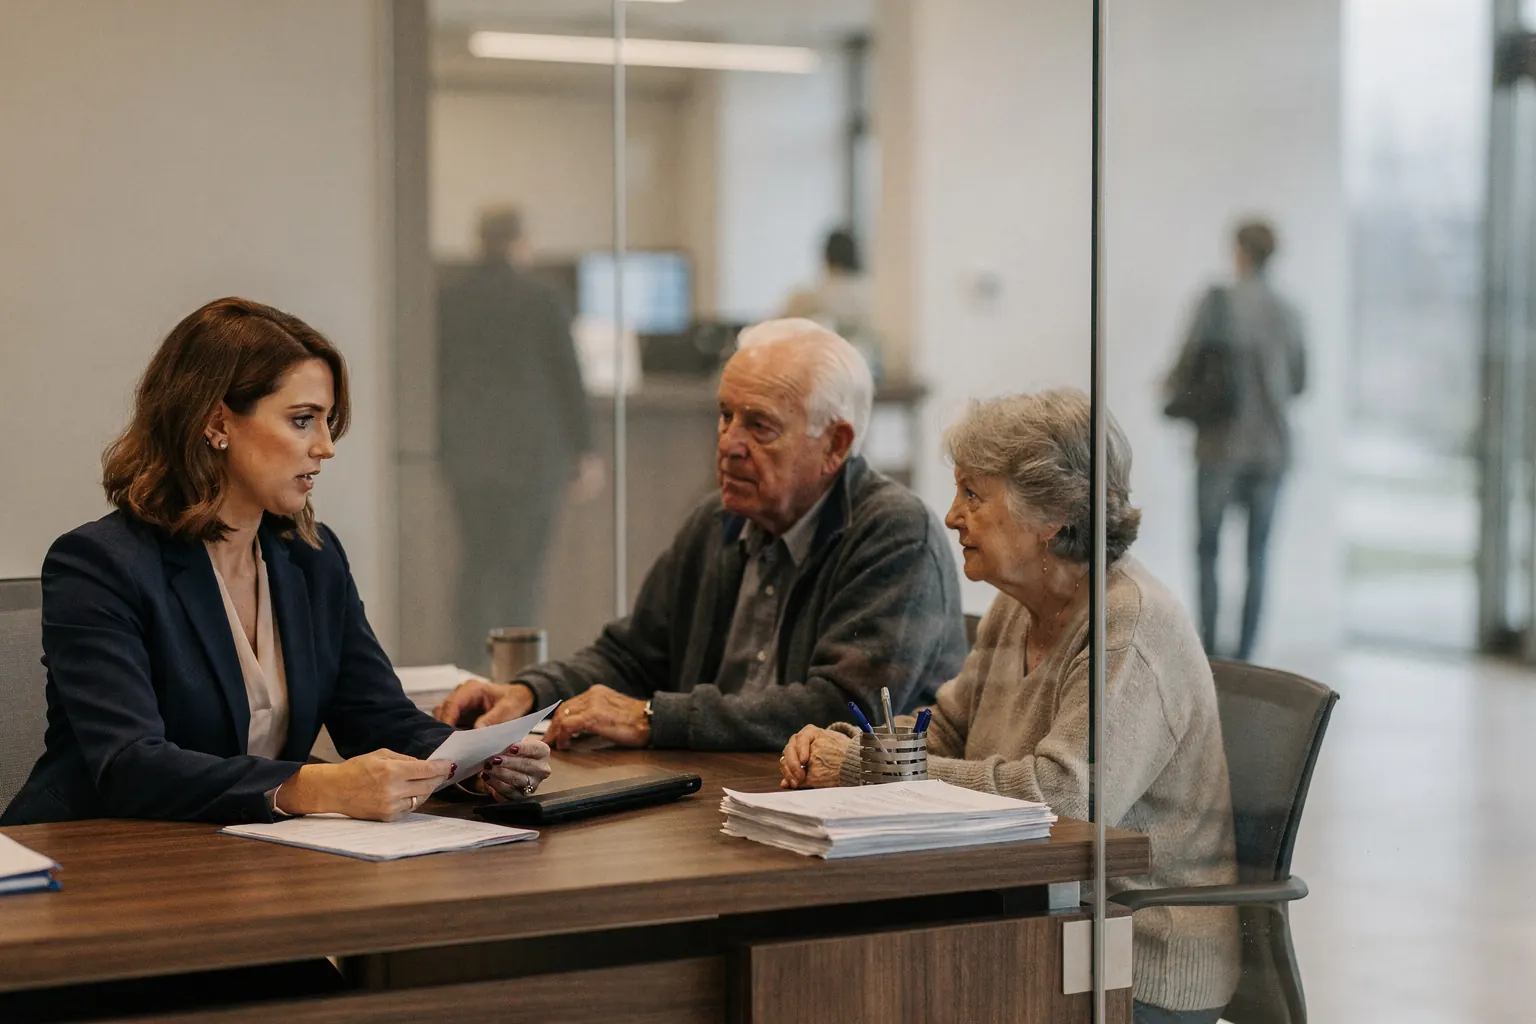
A community banker reviewing paperwork with an older couple in a glass-walled bank office
The Pressure

Where Financial Institutions Feel the Pressure

The threats are more convincing, the reporting deadlines are shorter, and the teams responsible for both are usually small.

01

Fraud now sounds exactly like your client.

1 in 4 malicious breaches were AI-enabled, a 56% increase in one year, with financial services among the most heavily targeted sectors.

(Source: IBM 2026 Cost of a Data Breach Report)

Cloned voices, deepfake video, and AI-written emails can now request a wire, a beneficiary change, or a distribution that looks and sounds routine. FinCEN has warned financial institutions directly about deepfake-enabled fraud. A verbal confirmation is no longer the safeguard it used to be.
02

Every regulator runs its own clock.

Banks have 36 hours to notify their primary federal regulator of a qualifying incident. Credit unions have 72 hours to notify NCUA. Michigan insurance licensees have 10 business days to notify DIFS. SEC-registered advisers have 30 days to notify affected clients under Regulation S-P. If you learn about an incident late, you lose time you were never going to get back.

  1. Banks 36 hours to notify their primary federal regulator
  2. Credit unions 72 hours to notify NCUA
  3. Michigan insurance licensees 10 business days to notify DIFS
  4. SEC-registered advisers 30 days to notify affected clients
03

Your vendors are part of your attack surface.

Core processors, custodians, agency management systems, and fintech integrations hold your most sensitive data outside your walls. Examiners expect you to know which vendors touch what, how they are monitored, and what happens when one of them has a bad day.

04

The exam playbook has changed.

The FFIEC retired its Cybersecurity Assessment Tool in August 2025 and pointed institutions toward NIST CSF 2.0 and CISA's performance goals. Both Regulation S-P compliance deadlines have now passed, and exams are underway. Documentation that satisfied the last exam may not satisfy the next one.

05

Small teams carry institution-sized obligations.

A community bank, credit union, or agency often has one or two people covering IT, security, and compliance in addition to their day jobs. The regulatory expectations do not scale down to match.

Every one of these pressures has a practical answer. Finding it starts with knowing where your institution actually stands.

Our Solutions

How Centaris Helps Financial Institutions Stay Secure and Exam-Ready

Stop impersonation fraud at the moment of approval

The most expensive fraud happens when a legitimate employee approves an illegitimate request. Centaris hardens the accounts and mailboxes attackers impersonate, and it builds out-of-band verification into money movement and account changes. We also train staff to recognize AI-generated voice, video, and email, so the approval step stays a real control instead of a formality.

Meet every notification clock with a plan that works

A written incident response plan is required almost everywhere in financial services. A tested one is rarer. We build response programs around your specific regulators, define who decides what and when, and run tabletop exercises so your team knows its role before a real clock starts.

Keep the controls examiners expect to see

Strong financial services security rests on a well-documented stack of controls:

Check what you have in place today

0 of 7 in place

Retain the records your regulators require

Books-and-records obligations reach into email, Teams chats, and client files. We configure Microsoft 365 retention, data loss prevention for nonpublic personal information, and message encryption, so what must be kept is kept and what must stay private stays private.

Use AI without exposing nonpublic personal information

Copilot and other AI tools can save your team real time on research, reporting, and client service. We prepare your Microsoft 365 environment first, tightening permissions and labeling sensitive data, so an AI assistant cannot surface a client's account details to someone who should never see them.

Put your IT provider inside your vendor oversight program

Your IT provider is one of the service providers regulators expect you to oversee. Centaris expects to be on your third-party risk list and supplies the documentation, incident commitments, and access records your vendor management program needs.

Secure every branch, agency office, and remote advisor

Branch networks, teller and producer workstations, and advisors working from home all need the same standard of protection. We segment networks, manage and encrypt devices through Intune, and verify every connection before it reaches client data.

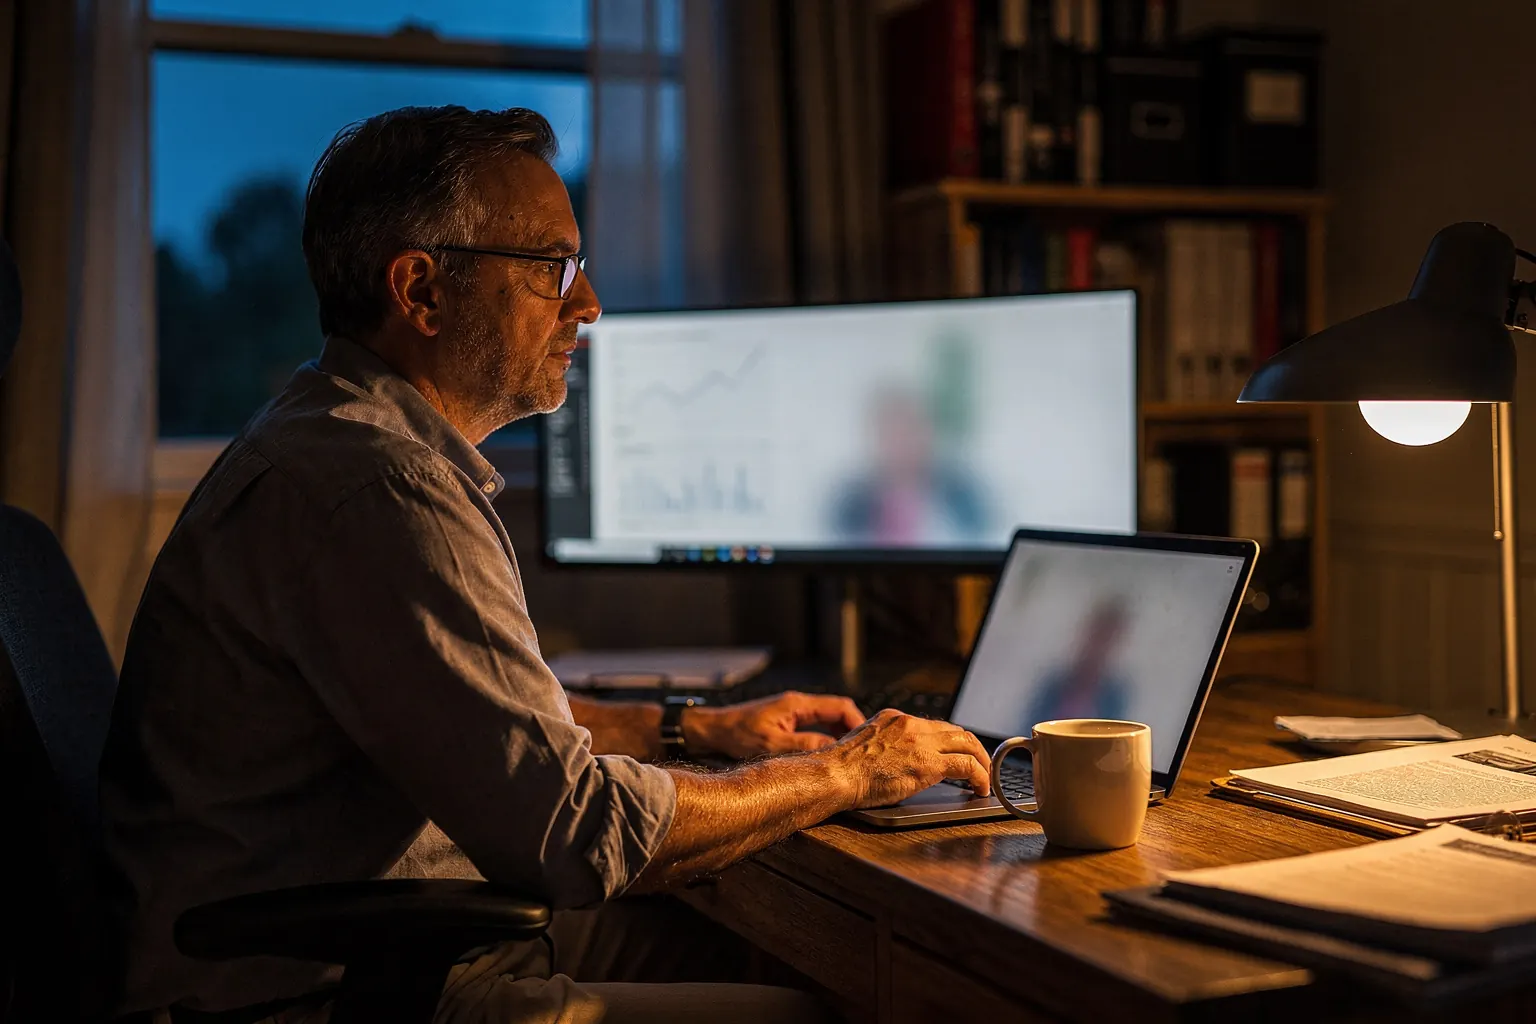
A financial adviser working from a home office in the evening

Add depth to a lean IT team

Centaris can run your IT and security end to end, or work alongside your existing IT staff and take on the monitoring, patching, and security work they have no time for. Either way, you gain engineers and security specialists who already know your environment and can be onsite when it matters.

Credit Unions

Security Built Around the Member Relationship

Credit unions share the obligations of every financial institution, plus a regulator, an exam program, and a member-owned governance model all their own. NCUA's 2026 resilience report shows how active the threat environment is. From May 2025 through April 2026, credit unions reported 588 cyber incidents to NCUA, including phishing, email compromise, ransomware, ATM jackpotting, and incidents that began at third-party providers.

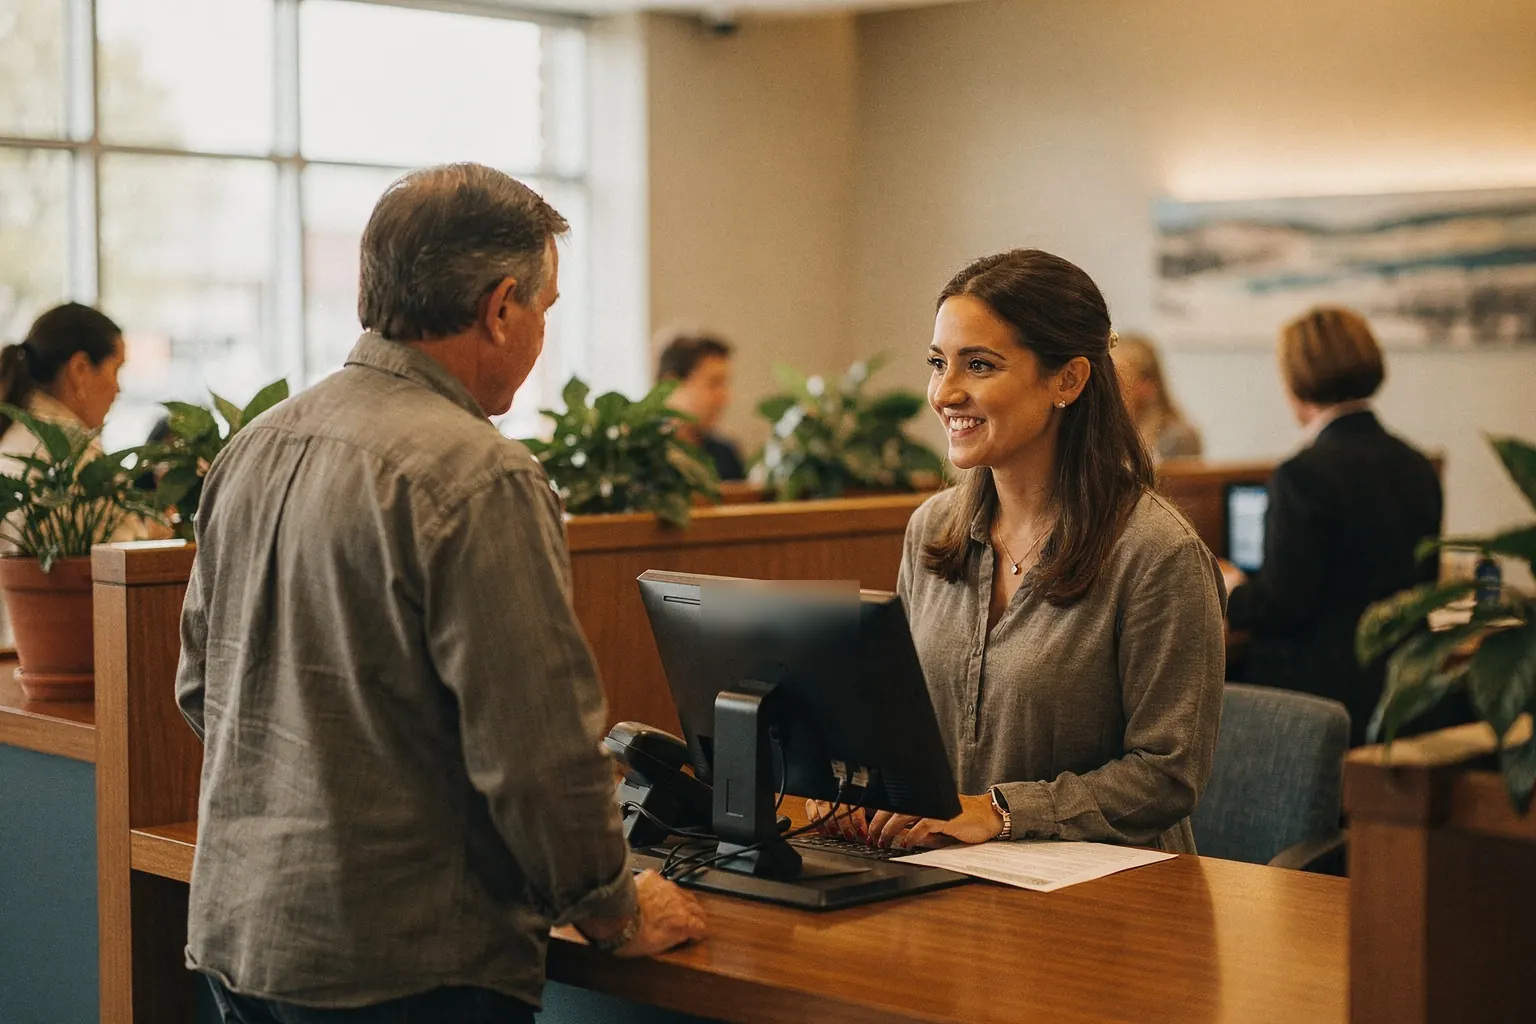
A credit union teller helping a member at an open teller pod

Meet the 72-hour rule, including when the incident starts at a vendor

The NCUA notification clock can start the moment a vendor tells you about its own incident. We help you build vendor notification paths, internal escalation steps, and a response plan that treats a third-party event with the same urgency as one inside your own network.

Prepare for your next ACET and information security exam

NCUA updated ACET in 2025 to incorporate NIST CSF 2.0. We help you map existing controls to the updated assessment, close the gaps examiners are most likely to raise, and organize evidence so the exam conversation stays focused and short.

Protect branches, ATMs, and member-facing systems

Attackers target the systems members touch every day. Centaris segments and monitors the networks your branches and ATMs run on, secures online and mobile banking dependencies you control, and watches for business email compromise, which credit unions reported to NCUA more often this past year than the year before.

Give your board a clear view of cyber risk

NCUA expects boards to engage directly in cybersecurity oversight. We translate technical findings into board-level reporting on risk, progress, and priorities, so directors can ask better questions and document informed decisions.

Exam Readiness

Examiners Want Evidence. Build It Before They Ask.

Whether you answer to the FDIC, OCC, Federal Reserve, NCUA, SEC, or DIFS, the expectation is a documented program that works in practice. Centaris moves through each stage with your team:

  1. Identify every regulator, rule, and contract obligation that applies, along with where nonpublic personal information lives and which vendors can reach it.

  2. Measure your controls against the framework your examiners use, whether that is NIST CSF 2.0, ACET, Regulation S-P, or the NAIC model law, and rank gaps by risk to customers and members.

  3. Put the highest-risk fixes in place first, coordinated with your core processor, custodians, and other critical vendors.

  4. Assemble the policies, logs, test results, and vendor records that show each control operating as designed.

  5. Deliver board and management reporting, prepare for each exam cycle, and update the program as rules and threats change.

When the examiner arrives, your team walks in with answers and documentation instead of a list of follow-up items.

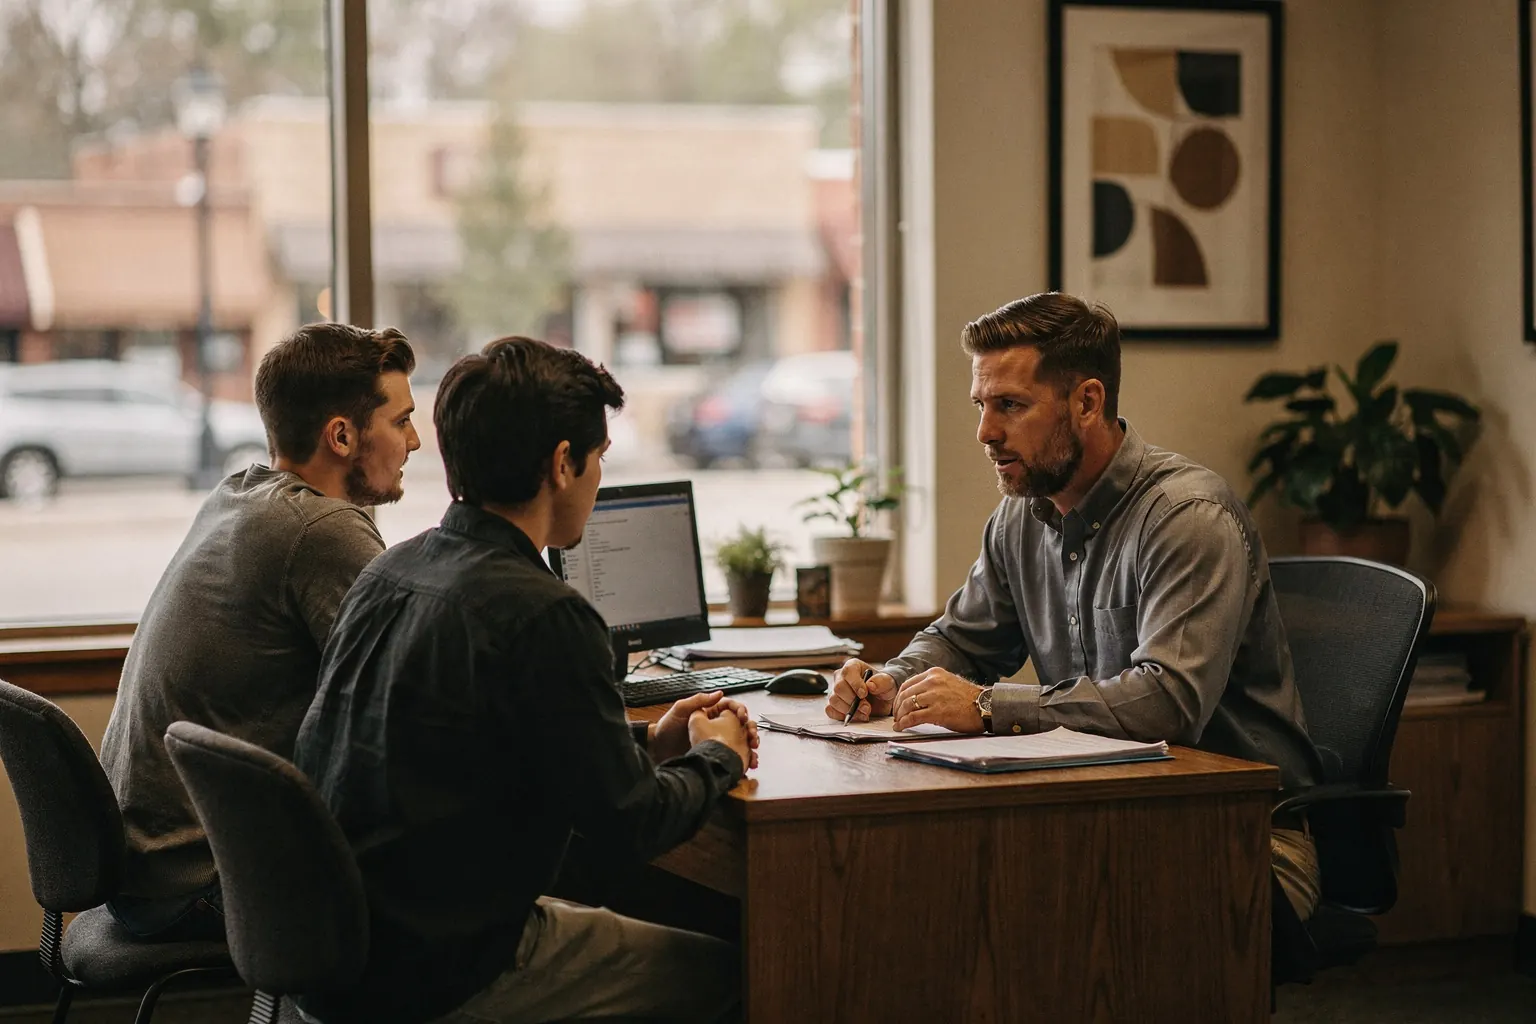
An independent insurance agent meeting with two clients in a small-town agency office
Our Differentiators

The Centaris Advantage in Financial Services

Financial institutions understandably ask harder questions of an IT partner than most organizations do.

We know what an examiner is going to ask.

Our work is shaped by the frameworks financial institutions are actually examined against, so the documentation we produce answers real exam questions.

We expect to pass your vendor review.

We provide the documentation, access controls, and incident commitments that belong in any critical vendor file, because an IT provider holding admin access to your systems should meet the same standard you do.

Your incident clock is our incident clock.

When a notification deadline is running, you work directly with Centaris engineers who know your environment, with no subcontractor between you and the answers.

We cover the branches as well as headquarters.

Engineers based across the region can be onsite at branches, agency offices, and operations centers when remote support is not enough.

We stay clear of roles that belong to others.

We are not your auditor, your examiner, or your compliance officer. We build and operate the security program they will evaluate, and we work openly with each of them.

Industry Impacts

Industry Impacts

Impact 01
$6.3M1

is the average cost of a financial services data breach, the second-highest of any industry. Much of that cost comes after the breach itself: investigation, notification, regulatory response, and lost relationships. Faster detection and a rehearsed response plan are the most direct ways to shrink it.

Impact 02
36 hours2

is how long banks have to notify their primary federal regulator after determining that a qualifying computer-security incident has occurred. That window leaves no time to find out who to call. Monitoring that catches incidents early and a plan that names the decision-maker make the deadline workable.

Impact 03
10 business days3

is the window Michigan insurance licensees have to notify DIFS of a qualifying cybersecurity event. Licensees with 25 or more employees must also maintain a written information security program. For independent agencies, that turns security from an IT preference into a licensing obligation.

1IBM 2026 Cost of a Data Breach Report; 2OCC, Federal Reserve, and FDIC Computer-Security Incident Notification Rule; 3Michigan Insurance Data Security Law (MCL 500.550 to 500.565).
Peace of Mind

When Your Last Provider Didn't Know What an Examiner Asks For

The stories we hear from financial institutions tend to repeat. A previous MSP answered an examiner's request with a generic SOC 2 report. An incident surfaced days late because no one was monitoring the logs. The IT provider held full admin rights but never appeared on the vendor risk list.

Situations like these are fixable. Centaris gives you a single, accountable team for IT operations and security, one that understands regulated finance and expects to be held to your standards.

Get Started

Know Your Exposure Before Your Examiner Does

A no-obligation assessment shows your leadership how your controls measure up against the rules you answer to, where vendor and fraud risk concentrate, and what to fix first.

Clear findings, practical priorities, and no commitment required.