Protecting the Confidences Your Firm Is Trusted to Keep
Every engagement starts with a client handing over something they would never make public: a merger strategy, a tax return, a litigation file, the floor plan of a secure facility. How your firm protects that information is part of the service, whether or not it appears on the invoice.
Centaris works with law firms, accounting and tax practices, consulting firms, and architecture and engineering firms across Michigan and the Great Lakes. We secure client information across Microsoft 365, the devices your people carry, and the AI tools they are already using. The goal is a firm that can show clients, carriers, and regulators exactly how their data is protected.
Security at a firm is never finished. Staff turn over, clients raise their requirements, and new tools arrive every quarter. We stay engaged as all three change, so your protections never fall a season behind.
Obligations are rising, and threats are getting more targeted, often in the middle of your busiest stretch of the year.
01 Client data is already flowing into AI tools nobody vetted.
4xgrowth in shadow AI activity detected in data loss prevention datasets, now the third most common non-malicious insider action.
(Source: Verizon 2026 Data Breach Investigations Report)
Staff paste contracts, tax records, and strategy decks into whatever tool is fastest. For law firms, ABA Formal Opinion 512 makes the confidentiality question explicit. For every firm, the exposure is the same: client data landing somewhere it was never meant to go.
1xPrior year
4x2026 report
02 Your clients are auditing you now.
Security questionnaires, outside counsel guidelines, vendor risk reviews, and cyber insurance applications all ask the same thing: prove it. MFA, endpoint protection, tested backups, and an incident response plan have moved from best practice to a condition of doing business.
Security questionnaires
Outside counsel guidelines
Vendor risk reviews
Cyber insurance applications
Prove it.
MFA
Endpoint protection
Tested backups
Incident response plan
03 Email is where the money moves.
Retainers, trust account disbursements, tax refunds, closing funds, and project payments all run through the inbox. That makes professional services firms a favorite target for business email compromise, where one convincing message redirects one large payment.
$Retainers
$Trust account disbursements
$Tax refunds
$Closing funds
$Project payments
The inbox
One convincing message
One large payment redirected
04 Regulators have named your profession.
Tax and accounting firms fall under the FTC Safeguards Rule. Lawyers carry a duty of reasonable security under ABA Model Rule 1.6(c). Design firms supporting defense work face CMMC. The rules differ, but each one expects documented, working controls.
Tax and accounting firmsFTC Safeguards Rule
LawyersABA Model Rule 1.6(c)
Design firms supporting defense workCMMC
05 Deadlines leave no room for downtime.
Tax season, trial prep, deal closings, and project submittals don't move because a server went down. Every hour your people can't work is an hour that doesn't get billed.
Tax season
Trial prep
Deal closings
Project submittals
What one outage costs in billable time
100billable hours lost
Each of these is manageable. What they require is a partner who knows how a firm operates between filing deadlines, trial dates, and project submittals.
Our Solutions
How Centaris Protects Your Firm and Your Clients
Adopt AI without putting client confidences at risk
Your staff are already experimenting, so the real decision is which tools earn approval and under what rules. Centaris helps you set that policy, prepares Microsoft 365 for Copilot, and applies sensitivity labels that keep privileged and confidential documents protected. We also train your people to increase productivity with AI without feeding client data into public models.
Answer client security reviews with evidence, not guesswork
When a client sends a 200-question security questionnaire, you should be able to answer it from documentation you already have. We put the controls, policies, and reporting in place so you can respond faster with accurate, consistent, and defensible information.
Stop fraud before the wire leaves
Business email compromise rarely needs malware. It needs one inbox, one lookalike domain, and one rushed approval. These controls take those openings away:
One inboxOpen
One lookalike domainOpen
One rushed approvalOpen
The wire leaves
Recovery
Keep client, matter, and engagement data where it belongs
Conflicts, ethical walls, and need-to-know access matter in professional services. We configure Microsoft 365 permissions and information barriers so teams see what they need and nothing more. We also make onboarding and offboarding clean, including seasonal staff, who should leave with nothing but their paycheck.
Team AClient A matter
Team BClient B matter
Protect the firm wherever your people work
Partners draft from home, staff split time between offices, and consultants work from client sites and airport lounges. Every login is verified, and every device is checked before it touches firm data, so location is no longer a security variable.
Get senior IT and security expertise without hiring it
Most firms have no reason to staff a security operations team. Centaris provides you with a Michigan-based team of engineers, security specialists, and Microsoft consultants who already know your environment. Hand us the whole IT function, or keep your internal IT staff and let us cover the gaps they cannot reach. You decide where the line sits.
Bring phones and client meetings into Microsoft Teams
Move your phone system into Teams so calls follow your people from office to home to client site. Teams Rooms make client meetings and hybrid conferences work the first time. It becomes one platform, secured and managed as part of the same environment.
Architecture & Engineering
Built for Design Firms That Work in Gigabytes and Deliver on Deadlines
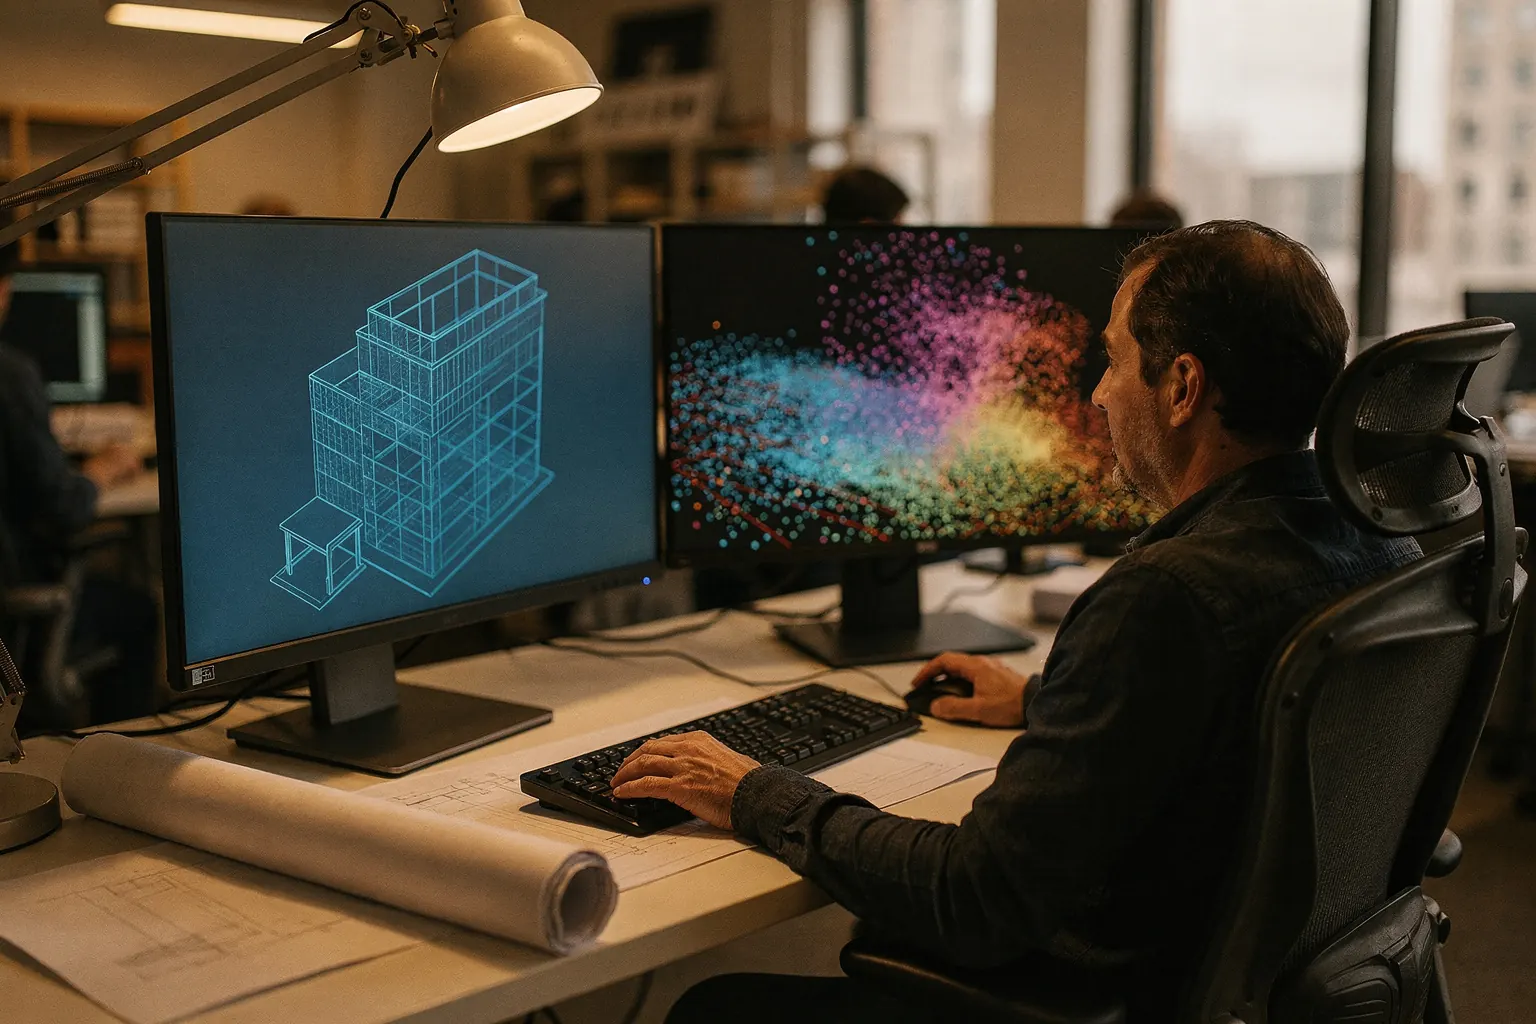
Architecture and engineering firms carry the same confidentiality obligations as every professional services firm, plus pressures that law and accounting offices never face. Your work lives in files measured in gigabytes. Your teams move between offices, job sites, and client locations. And a growing share of your clients are public agencies and defense programs with security requirements written directly into the contract.
Keep large project files fast, shared, and recoverable
Revit models, Civil 3D surfaces, and point clouds don't behave like ordinary documents. Centaris designs storage, collaboration, and backup around how design teams actually work. Multiple offices can share project files without workarounds, and a ransomware event means restoring last night's models instead of rebuilding a project from scratch.
Get ahead of CMMC on defense and federal projects
Design firms supporting Department of Defense projects often handle Controlled Unclassified Information in drawings and specifications. Phase 2 of the CMMC rollout, which would have added third-party Level 2 assessments as a condition of award, was suspended in July 2026 while the Department reviews the program. Phase 1 self-assessments are still required, and so is protecting CUI under NIST SP 800-171. We help you draw a boundary around the systems that touch CUI, implement the NIST SP 800-171 controls inside it, and assemble the evidence an assessor will ask for. When a formal assessment is required, it is performed by an accredited third-party organization or the government, not by us.
Firm networkEmailMarketingAccounting
CUI boundaryDrawingsSpecificationsNIST SP 800-171 controlsEvidence
Accredited third-party organization
Protect sensitive client designs
Floor plans for hospitals, schematics for utilities, and security layouts for plants and public buildings are valuable to the wrong people. We control who can access, share, and download sensitive project data, both within the firm and when it is shared with consultants and contractors.
Support the workstations and field teams that do the work
High-performance workstations, graphics drivers, design software licensing, and field tablets all need to work on day one of a project. We manage the full lifecycle, secure mobile devices on job sites, and keep your designers designing instead of troubleshooting.
Our Compliance Perspective
Confidentiality Is a Duty You Should Be Able to Prove
Your obligations may come from the ABA, the FTC, the IRS, client contracts, or the Department of Defense. Each one expects reasonable, documented security that holds up when someone asks to see it.
Obligation
Law firms
Accounting & tax
Consulting
Architecture & engineering
ABA Model Rule 1.6(c)
Applies
No
No
No
ABA Formal Opinion 512
Applies
No
No
No
FTC Safeguards Rule
No
Applies
No
No
IRS
No
Applies
No
No
Client contracts
Applies
Applies
Applies
Applies
Cyber insurance applications
Applies
Applies
Applies
Applies
CMMC (Department of Defense)
No
No
No
In some cases
Applies Half mark: applies to design firms supporting defense work.
Here is how Centaris gets a firm from uncertain to answerable:
Answerable
Uncertain1/5
1
Inventory & Scope
Identify where client data lives, how it moves, and which obligations apply to your firm, from ABA Model Rule 1.6(c) and the FTC Safeguards Rule to client security terms and CMMC.
2
Assess
Measure your current controls against those obligations and rank the gaps by how much client data each one leaves exposed.
3
Remediate
Fix what matters most first, with changes scheduled around your deadlines rather than on top of them.
4
Document
Build the written information security plan, incident response plan, policies, and questionnaire-ready evidence that your clients, carriers, and regulators expect.
5
Review
Revisit controls, retrain staff, and refresh documentation on a regular cadence, so the next client audit or insurance renewal is a routine exercise.
The outcome is a security program you can explain in plain terms to a managing partner, a client, or an underwriter.
Our Differentiators
Why Professional Services Firms Choose Centaris
We treat client data like the asset it is.
Your reputation depends on confidentiality. We design access, sharing, and AI controls around that reality, not around a generic office template.
Security questions go to people who know your firm.
Centaris keeps its cybersecurity team on staff. If an incident hits, the engineers responding have seen your environment before, and there is no outside call center in the middle.
Microsoft is the foundation, not an add-on.
Identity, email, documents, Teams, and Copilot are configured and protected as one system, so the licenses you already pay for do more of the security work.
We plan around your calendar.
Major changes are scheduled around filing deadlines, trial dates, closings, and project milestones. Your busy season is our planning input, not an inconvenience.
We tell you where our role ends.
We are not your ethics counsel, your peer reviewer, or your CMMC assessor. We build the environment, documentation, and evidence that people will review, and we bring in outside specialists when an engagement requires them.
Industry Impacts
Industry Impacts
Impact 01
29%1
of law firms reported having experienced a security breach, and another 19% didn't know whether they had. A firm that can't answer that question can't answer a client's either. Logging, monitoring, and a tested incident response plan turn "we think we're fine" into a real answer.
Reported a breach 29%
Didn't know 19%
Impact 02
$3.05B2
in business email compromise losses were reported to the FBI in 2025 across 24,768 complaints. That averages roughly $123,000 per complaint, often a single redirected wire, retainer, or project payment. MFA, email authentication, and a verified payment process close most of that gap.
$3.05B÷24,768 complaints=~$123,000 per complaint
Impact 03
30 days3
is how long tax and accounting firms covered by the FTC Safeguards Rule have to notify the FTC after discovering a breach of unencrypted information involving 500 or more consumers. The clock starts at discovery, so detection and a working response plan decide how much of that time you actually have.
DiscoveryNotify the FTC
1ABA 2023 Cybersecurity TechReport;2FBI IC3 2025 Internet Crime Report;3FTC Safeguards Rule (16 CFR Part 314).
Peace of Mind
If Your Last Provider Treated You Like Any Other Office
Firms often reach out to us for the same reasons. A previous MSP handled passwords and printers but called the client security questionnaire "not our area." An outage landed in the middle of tax season. A spoofed email redirected a payment, and the provider wrote it off as user error.
Many firms have lived some version of that. Centaris takes the opposite position: IT operations and security sit with one accountable team that understands professional services, so there is never a question about who owns the problem.
Get Started
See Where Your Firm Stands
A no-obligation assessment shows your leadership which client data is exposed, which controls are working, and what your clients, carriers, and regulators are likely to ask for next. You get the findings before a questionnaire, renewal, or incident sets the timeline for you.
One conversation. Straight answers. Your decision on what comes next.